
How Anyone Can Check a Badge
A badge you can copy is worth nothing, so ours are built to be checked.
1. Click it
Every genuine badge links to a page at www.chaindefenders.xyz/verify/... that shows the project it was issued to, its website, what it certifies, and whether it is still valid.
- The name or website is not the site you are on? The badge was copied.
- The link goes anywhere else, or nowhere? It is not our badge.
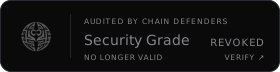
- It says revoked? Do not rely on it.
2. Check the signature
The facts on the verify page are signed with our Ed25519 key, so you do not have to trust the page itself.
- On the verify page, press Check the signature in your browser. Your browser downloads the signed facts and our public key and checks them itself.
- Or check it yourself: the signed facts are at
www.chaindefenders.xyz/api/badge/BADGE-IDand our public key atwww.chaindefenders.xyz/api/badge/key. The signature (base64url) covers the facts as JSON with keys sorted and no spaces. The verify page has a command that does this with Node.js.
3. Match the report
For a Security Badge, the verify page shows the SHA-256 fingerprint of the final report and the commit we reviewed. If you have the report, its fingerprint should match. If you have the code, compare the commit with what is deployed.
The details
- Each badge has its own random address that cannot be guessed. Its verify page is not listed anywhere or indexed by search engines; it is reached through the badge.
- When the facts change, the badge is signed again; older signed versions stay checkable at
/api/badge/BADGE-ID?seq=1,?seq=2and so on.
- Revoking a badge changes its image and its page within five minutes, wherever it is shown.